Validating Our Commitment to Information Security and Swiss Data Sovereignty
KEMARO earns ISO/IEC 27001 certification.
KEMARO has been now certified to ISO/IEC 27001:2022, the leading international standard for information security management. An independent audit by ccSec (Certification Center Security, accredited by DAkkS, confirmed that KEMARO manages information security through a defined, monitored, and continually improved management system.
The certification covers software development, operations, IT administration, and the ongoing development of KEMARO's product and cloud application platform (KEMARO Sphere).
How KEMARO Connects
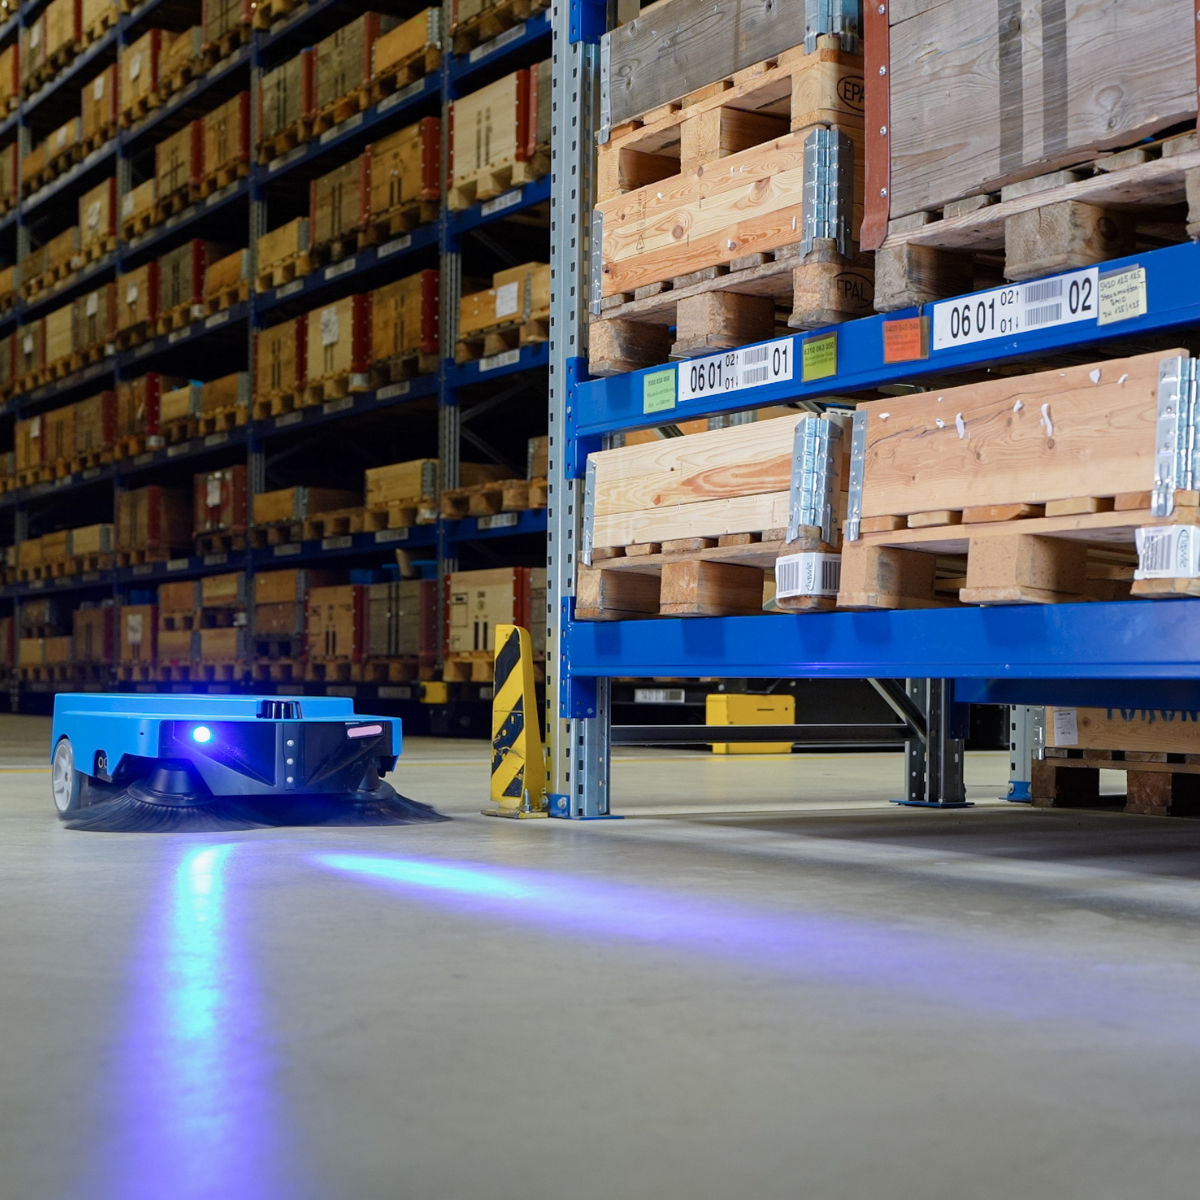
KEMARO's autonomous industrial sweepers do more than clean. They connect.
Maps, cleaning schedules, live status, and fleet telemetry move between the robot, KEMARO Sphere, and our support team over the cloud, with over-the-air updates and remote maintenance. As part of that ongoing commitment, independent auditors have reviewed how KEMARO handles this data against ISO/IEC 27001, the leading international standard for information security management.
As part of maintaining that commitment, certification required KEMARO to:
- Strengthen security against cyber threats by identifying potential attack vectors early and establishing appropriate protective measures for the product, the Sphere cloud platform, and company processes.
- Define, monitor, and measure the controls that manage those risks.
- Run internal audits and a continual-improvement process that adapts as risks change.
- Pass an external, third-party audit conducted by an accredited body.
Customers gain assurance that security risks are systematically managed, and that their data, systems, and processes are protected when using the Sphere platform.
Why it matters
Autonomy means connectivity, and connectivity raises a fair question from every serious operator: what happens to our data? KEMARO's answer has not changed, it is now certified.
- Certified trust. Instead of a marketing claim, customers get audited assurance: a documented information security management system, reviewed by an accredited third party and maintained through annual surveillance audits.
- Swiss data sovereignty, by design. KEMARO's servers are located in Switzerland, KEMARO robots reduce onboard sensors to limit what is captured, and the platform is built for European and Swiss data-protection compliance. ISO/IEC 27001 formalises the governance around that data; from the robot, through Sphere, to remote support.
- Enterprise-ready connected robotics. For IT, information security, and procurement teams evaluating a connected robot, an ISO/IEC 27001 certificate is a recognized reference point - audited evidence they can build their own vendor review around.
What ISO/IEC 27001 is
ISO/IEC 27001 is the leading international standard for information security management. Certification means an accredited, independent body has audited how an organisation identifies information security risks and manages them through a defined set of controls and confirmed that the system meets the standard. The certificate is maintained through annual surveillance audits over a three-year cycle.
The certification does not replace a customer's own obligations, and it is not a claim that any system is immune to every threat. It is confirmation of something more durable: a systematic, audited approach to managing information security risks, and a commitment to improving it over time.
Security is not a feature we added; it is how we engineer. Achieving ISO/IEC 27001 certification confirms that KEMARO manages information security to an international standard as we scale past 1,500 robots in 40 countries. It gives every customer, in every market, a certificate to point to.” - Armin Koller, CEO
Learn more
To discuss what the certification means for your facility, talk to our team.
Scopri di più